RA5olver

NIST SP 800-53 · RA-5 Vulnerability Monitoring and Scanning

Governed AI for federal vulnerability management.

RA5olver places verification between AI and the analyst, so every recommendation on an RA-5 vulnerability decision arrives with its evidence status. Analysts rely on what the record supports and question what it does not.

Start a conversation ian@ra5olver.com

Licensing for federal agencies and their partners is coming.

Finding 0142dc01.example192.0.2.10
CVE-2020-1472
Netlogon elevation of privilege
AI recommendation, as the analyst sees it
  • Listed in the CISA Known Exploited Vulnerabilities catalog. Verified CISA KEV catalog
  • Severity is moderate, CVSS 5.5. Defer to the next patch cycle. Contradicted NVD · NIST base score 10.0, Critical
  • A compensating control is documented for this host. No record No matching record in the evidence store
Illustrative example. Vulnerability data from NVD and CISA KEV. The host is fictional.

The problem

Findings arrive faster than evidence can be checked.

Scanners find vulnerabilities faster than analysts can adjudicate them. AI assistance promises relief, but fluent output with no link to the authoritative record leaves the analyst guessing at the moment of decision, and errors pass through as easily as good answers.
How RA5olver works

The evidence speaks before the analyst decides.

Verified before it is shown

Each AI output is checked against the authoritative evidence record before it reaches the analyst.

Status at the point of decision

The analyst sees whether the record supports an output, contradicts it, or holds nothing on it.

Honest about gaps

When an output cannot be verified, RA5olver says so plainly rather than filling the gap.

Inside your boundary

Licensed software designed to install on your own infrastructure and work alongside the scanners and models you already use.

Grounded in research and practice

Built by someone who has worked the queue.

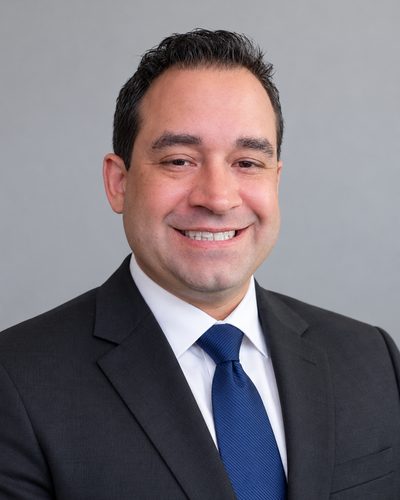
Portrait of Dr. Ian Rivera, founder of RA5olver

RA5olver grows out of doctoral research on governed communication and appropriate reliance in NIST SP 800-53 RA-5 vulnerability management, and out of nine years as a contractor supporting vulnerability remediation, assessment and authorization, and continuous monitoring for the U.S. Department of the Interior.

Dr. Ian Rivera
Founder, RA5olver LLC

RA5olver is in active development.

We welcome conversations with federal agencies, cloud service providers, and defense contractors about licensing and early evaluation.